

Businesses urged to tighten AI governance beyond awareness
Mon, 12th Oct 2026 (Today)
Cyber Security Awareness Month has sharpened debate over whether companies need to move beyond staff awareness campaigns and strengthen governance around artificial intelligence and operational technology. Industry executives say the focus is shifting to human oversight, resilience and practical action.
Cyber security and resilience specialists say businesses now face a broader set of risks as AI tools spread into everyday work and digital systems become more closely tied to physical operations.
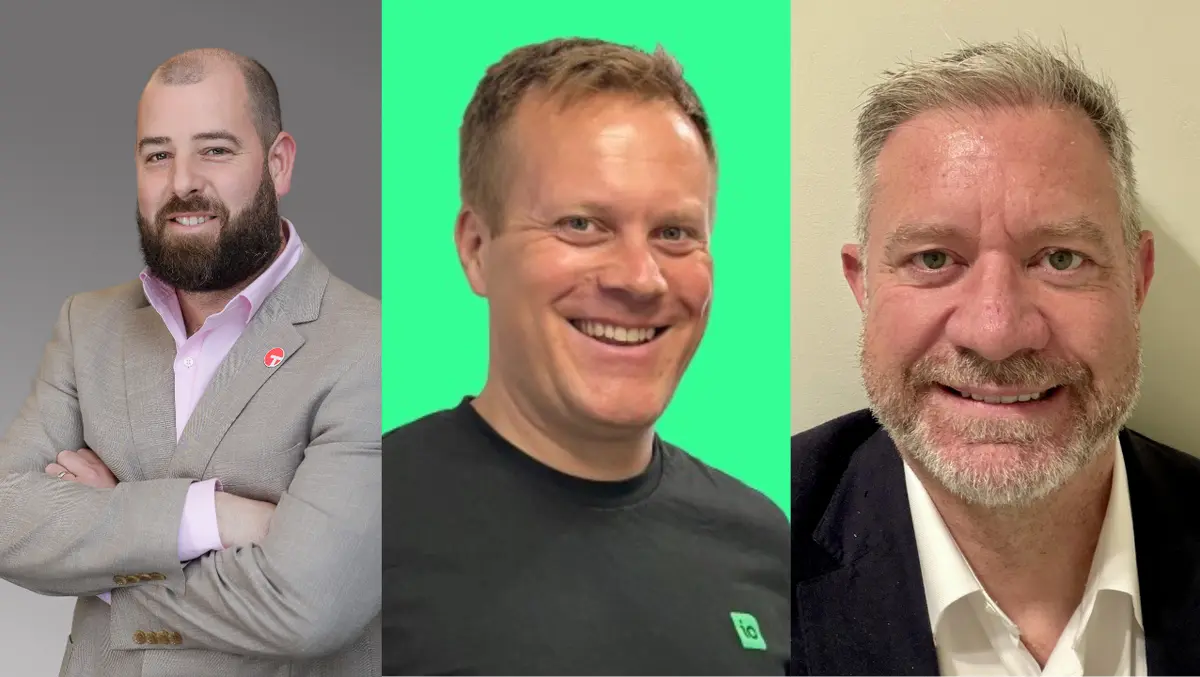
James Greenwood, Area Vice President, Solution Engineering APAC at Tanium, said many organisations are still at an early stage in how they use AI for cyber operations and decision-making.
"This year, the ASD is calling for an inaugural year of action, and for good reason. Many businesses are already using AI to uncover insights on market opportunities, growth prospects and, of course, cyber threats. But few are actually using AI to turn those insights, dashboards and data into tangible action. This gap will separate AI experimenters from AI adopters, with the latter best equipped to turn noise into action plans specific to their roles.
He said the spread of AI tools has changed access to cyber and IT guidance across organisations.
"We're now in a world where both skilled and less skilled operators can enter a prompt about an IT or security issue and get real-time guidance on how to address it. That reduces the need for highly skilled resources and democratises access to tools. Management has never had greater access to real-time reporting and visibility, along with guidance on how to investigate, mitigate and remediate issues as they happen.
"Taking effective control of these new capabilities requires companies to pair AI adoption with a 'human above the loop', not just a 'human in the loop'. We can't assume that equipping teams with AI will lead to good governance. Businesses need a proactive approach to keeping humans in control of how AI is used, designed and evolved over time. That means being willing to change, stop or update AI tools and approaches as needed, and investing the time and resources to ensure they support and strengthen cyber hygiene without introducing new business or governance risks," Greenwood said.
Governance shift
Sam Peters, Chief Product Officer, IO, said AI is moving security decisions beyond dedicated cyber teams and into day-to-day business processes.
"AI is changing who makes security decisions inside a business. Decisions about which tools to use, what information to put into them, and which suppliers or systems to connect are increasingly being made as part of everyday work, not just by security teams.
"That makes good governance far more important. Organisations cannot rely on every employee recognising every security or compliance risk as it arises. They need a framework around those decisions: clear ownership, approved tools, sensible controls, visibility over what is being used, and a straightforward way to escalate something that does not look right.
"Our latest State of Information Security report found that 40% of organisations see AI systems making decisions or taking actions without human oversight as a security challenge. The answer is not to put the brakes on AI. It is to have the governance in place to use it with confidence.
"Cybersecurity awareness still matters, but it works best as part of that wider system. People make better decisions when the organisation has already given them clear boundaries, accountability and support," Peters said.
Physical risks
Jason Pearce, Field CTO, APJ, Claroty, said the discussion also needs to account for operational technology and cyber-physical systems that underpin essential services.
He said organisations in sectors such as utilities, healthcare, manufacturing and transport need to think beyond phishing and passwords and consider what would happen if digital disruption affected physical operations.
Pearce pointed to dependencies across electricity, water, transport, hospitals, food supply chains, data centres and manufacturing systems. Disruption in those environments can spread beyond a single organisation and affect suppliers, customers and communities.
This has pushed cyber security leaders and boards to focus more closely on system criticality, remote access, dependencies and recovery. It has also widened the conversation from attack prevention to continuity under compromised conditions.
The common theme across these views is that awareness alone is no longer enough. Business leaders are being urged to combine user education with AI governance, stronger human oversight and a clearer understanding of which systems matter most when disruption hits.
For companies whose digital environments now shape frontline operations, the central question is whether they can continue running safely when systems fail or need to be isolated for an extended period.